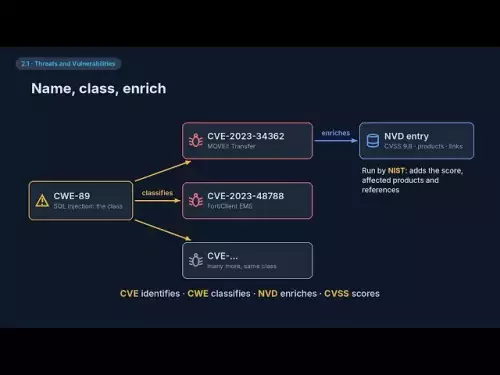
I learn best from visual diagrams paired with narration, so I used Claude and Amazon Polly to make these videos for my own Security+ study, and figured I'd share them for anyone else who learns the same way. The content was built from long, chained deep-research sessions across Claude, ChatGPT and Grok on their top-tier plans, and mapped to the official SY0-801 exam objectives. Because it's AI-researched, treat CompTIA's official objectives as the final word on any detail. Narration is AI-generated. Not affiliated with or endorsed by CompTIA. If they help, a like or subscribe is appreciated, and comment if there's another topic or cert you'd like made in this style. Part 2 of a CompTIA Security+ SY0-801 (V8) video course with Network+ fundamentals woven in. 39 episodes, one chapter each. Chapters: 0:00 2.1a - Threat, Vulnerability, Exploit and Risk 4:15 2.1b - Threat Intelligence Sources, Feeds and Life Cycle 8:31 2.1c - CVE, CVSS and Vulnerability Prioritization 13:38 2.2a - Threat Actors and Their Attributes 18:37 2.2b - Threat Actor Motivations 23:06 2.3a - APTs and Message and Image Lures 27:46 2.3b - Attachments and the Browser 31:46 2.3c - Network, Remote Access and Endpoint Vectors 36:43 2.3d - Supply Chain, Removable Media and People 40:41 2.3e - IoT, OT, Physical and Signal Vectors 45:06 2.4a - The Unmanaged and the Forgotten 49:51 Net+ N04 - Wireless Networking, WPA2 vs WPA3 and 802.1X 56:14 2.4b - Ports, Services and Wireless Weaknesses 1:00:52 Net+ N05 - HTTP Requests, Cookies and the Same-Origin Rule 1:05:59 2.4c - Injection Attacks, When Data Becomes Code 1:10:18 2.4d - XSS, Request Forgery and Directory Traversal 1:15:25 2.4e - Buffer Overflows, Race Conditions and Malicious Updates 1:19:58 2.4f - Code, OS, Virtualization and Crypto Weaknesses 1:24:16 2.4g - Cloud, Identity, Mobile and LLM Attack Surfaces 1:28:24 2.5a - Malware by Behavior 1:33:36 2.5b - Physical Attacks 1:37:04 2.5c - DDoS and Protocol Downgrade Attacks 1:42:00 Net+ N06 - IP Addressing, Subnets, CIDR and NAT 1:47:51 Net+ N07 - Switching and ARP, How a Packet Leaves Your Laptop 1:53:12 2.5d - Sniffing, Spoofing and On-Path Attacks 1:58:29 Net+ N08 - DHCP, DORA, Leases and Relays 2:03:36 2.5e - Rogue DHCP, Rogue Access Points and Evil Twins 2:08:42 Net+ N09 - DNS Deep Dive, Resolvers, Records, DNSSEC and DoH 2:14:29 2.5f - DNS Attacks and Cache Poisoning 2:19:20 2.5g - Social Engineering from Phishing to Deepfakes 2:24:04 2.5h - Indicators of Compromise 2:28:52 2.5i - Application Attacks from the Defender's Chair 2:33:35 2.5j - Credential Attacks and MFA Bypass 2:37:47 P02 - PBQ Walkthrough on Naming the Attack from Evidence 2:43:54 2.6a - AI Model Attacks, Manipulation, Poisoning and Evasion 2:48:29 2.6b - Prompt Injection, Jailbreaks, Code Execution and Session Hijacking 2:53:19 2.6c - AI Data and Trust Risks 2:58:21 2.6d - The AI Threat Decision Tree 3:02:10 R2 - Domain 2 Review, Threats, Vulnerabilities and Attacks Narration: Amazon Polly (Nate). Animated diagrams generated for this course.
The information provided is not trading advice. kdj.com does not assume any responsibility for any investments made based on the information provided in this article. Cryptocurrencies are highly volatile and it is highly recommended that you invest with caution after thorough research!
If you believe that the content used on this website infringes your copyright, please contact us immediately (info@kdj.com) and we will delete it promptly.